Microsoft SQL Database Audit Logs
You can track database administrative activity through Microsoft SQL Server for log search and basic detection rules (formerly known as custom alerts) on Windows machines.
Before You Begin
Complete these requirements before you start:
- Review Microsoft SQL Server Audit documentation to understand how auditing works.
- Confirm you have administrator privileges on the SQL server.
- Ensure the service account has access to the Windows Security or Application log. To grant access, add the service account to the Event Log Readers group.
Add the service account to the Event Log Readers group
SIEM (InsightIDR) uses the service account to read the Windows Security and Application logs. Add the account to the local Event Log Readers group on the SQL server to grant this access.
To add the service account to the local Event Log Readers group:
- Open Computer Management by pressing Win + R, entering
compmgmt.msc, and then pressing Enter. - From Computer Management, select System Tools > Local Users and Groups > Groups.
- Double-click Event Log Readers.
- From the Event Log Readers Properties dialog, select Add.
- In the Enter the object names to select field, enter the service account name in the format
DOMAIN\ServiceAccountName. - Select Check Names to confirm the account name resolves.
- Select OK twice.
Enable auditing on the SQL Server database
To enable auditing, configure the Windows audit policy, create a server audit, and then create a server audit specification.
To enable auditing of the SQL server database:
- Open a command window to configure the audit object access setting.
- Run the following command as an administrator:
auditpol /set /subcategory:"application generated" /success:enable /failure:enable - Run the following command to grant the generate security audits permission to an account:
secpol.msc - Go to the Local Security Policy tool and open Security Settings > Local Policies > User Rights Assignment.
- In the results pane, double-click Generate security audits.
- On the “Local Security Setting” tab, click Add User or Group.
- In the “Select Users, Computers, or Groups” dialog box, enter the name of the account SQL Server is running as and click OK.
- Restart SQL Server to enable this setting.
- To create a server audit, open SQL Server Management Studio.
- In “Object Explorer,” expand the Security folder.
- Right-click the Audits folder and select New Audit.
- Fill in the fields and choose either Windows Application log or Windows Security log as the audit destination.
Event Log Readers access required for Windows Security log
To audit the Windows Security log, the service account must be a member of the Event Log Readers group on the SQL server.
- When you are finished, click OK.
- Right click the newly created Audit and select Enable Audit.
- To create a server audit specification, go to “Object Explorer” and click the plus sign to expand the “Security” folder.
- Right-click the Server Audit Specifications folder and select New Server Audit Specification.
- Enter a name, choose the server audit created above, and configure the audit action types you want to log.
- For example, you could log the following:
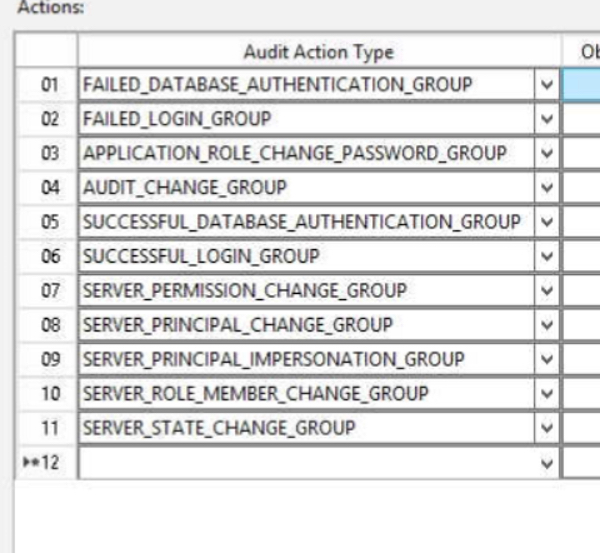
- When you are finished, click OK.
- Right click the newly created Audit Specification and select Enable Audit Specification.
Testing
After enabling SQL Server database auditing, follow these steps to verify that WMI and DCOM are functioning properly.
Test WMI Rights
- On the SQL server, run
wmimgmt. - Open root and highlight
cimv2. - Click Security and confirm the rights:
- Execute Methods
- Enable Account
- Remote Enable
- If a WMI browsing tool is available from the Collector, you should now be able to connect and browse
cimv2.
Test DCOM
- On the SQL server, run
dcomcnfg.exe. - Under Component Service, open Computers.
- Right click My Computer > Properties > COM Security tab.
- Under Launch and Activation Permissions, click Edit Limits.
- Confirm Remote Launch and Remote Activation are enabled.
Configure SIEM (InsightIDR) to collect data from the event source
After you complete the prerequisite steps and configure the event source to send data, you must add the event source in SIEM (InsightIDR).
To configure the new event source in SIEM (InsightIDR):
- Click Data Connectors in the left menu, and navigate to SIEM > Data Collectors. Click Setup Event Source > Add Event Source.
- Click Add Raw Data > Database Audit Logs.
- Alternatively, you can search for Microsoft SQL Server or filter by the Database Product Type, and then select the Microsoft SQL Server event source tile.
- Choose your collector. You can also name your event source if you want.
- Choose the timezone that matches the location of your event source logs.
- In the Server field, enter the IP address or the machine name of the server.
- In the User Domain field, enter the the domain of your credentials.
- Select existing credentials or create a new credential.
- In the Password field, enter the password for the SQL server.
- Click Save.
No Default Alerts
Database audit logs do not have alerts built-in by default. You must create your own alerts.