Welcome to Standalone Managed Digital Risk Protection (Managed DRP)
This page outlines the Managed Digital Risk Protection information related to the Standalone Service.
Rapid7 Standalone Managed DRP
Rapid7’s Standalone Managed DRP is a Threat Intelligence solution that combines advanced technology with expert analyst support. It safeguards your critical digital assets and data from external threats, while also providing guidance and remediation where appropriate.
Standalone Managed DRP uses the Digital Risk Protection (Threat Command) to provide visibility across the clear, deep, and dark web. This enables early detection of potential attacks or data leaks, helping to stop threats sooner and take action to protect your digital assets in real time. While it runs on the same Digital Risk Protection (Threat Command) engine, this is a new standalone product with no integration or intervention from Rapid7 tools. All alerts and triage are managed directly through your platform, supported by the Rapid7 Managed DRP team.
Standalone Managed Digital Risk Protection Scope of Service
Managed DRP Team
Managed DRP Onboarding Specialist
The Managed DRP Onboarding Specialist is responsible for guiding you through the onboarding process, helping you understand how the service operates, become familiar with the Digital Risk Protection (Threat Command) platform, and access support when needed. They will assist with basic tuning, configure necessary integrations with InsightIDR, and ensure your service is properly initiated. Once the technology is fully operational and your initial contextual information has been collected and integrated into your Digital Risk Protection (Threat Command) instance, your organization will have reached the stage of active monitoring.
Managed DRP Analyst
The primary function of the Managed DRP Analyst is to review and triage alerts in your Digital Risk Protection (Threat Command) instance to ensure they are as accurate and actionable as possible, while minimizing noise such as false positives. It is important to note that the accuracy of any threat/alert is heavily influenced by the uniqueness and clarity of your assets and the contextual information you provide, so some level of regular tuning and review will be required.
‘Ask the Analyst’
Rapid7’s Digital Risk Protection (Threat Command) “Ask the Analyst” service provides expert guidance, additional context, and recommended remediation steps. The team can also execute dark web purchases or initiate engagement with threat actors related to existing alerts. They respond to inquiries submitted through the Ask-an-Analyst chat box, using a wide range of tools and techniques to investigate and uncover new intelligence.
You may also submit a case through the customer portal to request information on significant global cyber events, investigate specific email addresses, review dark web mentions in our database, or obtain deeper insights into threat actors. The Ask the Analyst service is available 24/7.
| Response Trigger | Time to Action | Action |
|---|---|---|
| Urgent Intel Request | 2 hours | To provide an initial response to an urgent request from the customer’s team made via the ‘Ask an Analyst’ chat or customer portal. |
| Non-urgent Intel Request | 6 hours | To provide an initial response to a non-urgent request from the customer’s team made via the ‘Ask an Analyst’ chat or customer portal. |
Remediation Service Team
As organizations adopt new digital channels to engage with customers, cybercriminals adapt by impersonating well-known brands, launching scam campaigns, and exploiting unsuspecting consumers. Rapid7’s remediation team provides external enforcement services to take down content that impersonates your brand, infringes on trademarks or copyrights, and poses a threat to your customers. Digital Risk Protection (Threat Command)’s in-house automated Remediation Services streamline and accelerate the takedown of malicious or harmful web content targeting your brand.
| Response Options | Quantity | Description |
|---|---|---|
| Remediation Requests | Limited to 50 requests per year *Additional bundles available | Request that Rapid/ contact a content provider and act on your behalf to remove a threat from the Internet. The success of a remediation request is dependent on the proper preparation and submission of evidence. Rapid7 will help you collate and prepare the evidence to make a formal request. |
| Dark Web Purchases | Limited to 50 per year *Additional bundles available | Rapid7 offers secure and anonymous clear and dark web purchases made on your behalf. To request a purchase, use the “Ask an Analyst” button in the dashboard. |
In-Scope Service Components
Managed DRP is built around Rapid7’s Digital Risk Protection (Threat Command) platform, which delivers proactive defense by transforming threat intelligence into actionable insights.
Digital Risk Protection (Threat Command) leverages ground-breaking data-mining algorithms and unique cyber reconnaissance capabilities to continuously scan the clear, deep, and dark web to deliver actionable, contextual reconnaissance about potential threats to your organization, employees, executives, and board members. It integrates with our existing security solutions to highlight operational vulnerabilities, secure data, and protect your resources. This, combined with additional findings and expertise from the Threat Intelligence Analyst team, provides comprehensive protection for your organization.
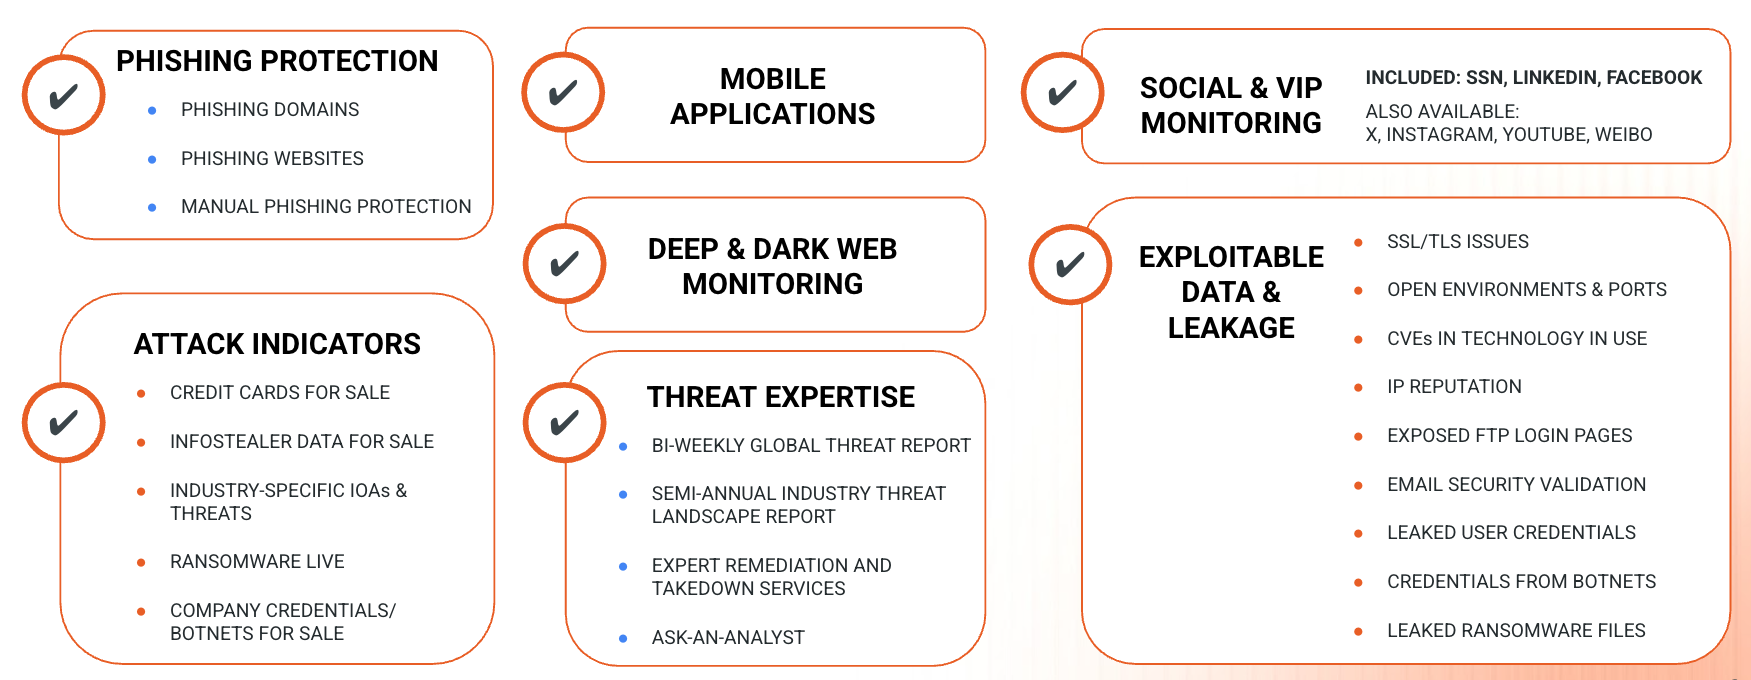
Managed DRP incorporates the following components of Digital Risk Protection (Threat Command).
Technology
The Rapid7 Managed DRP service is powered by Digital Risk Protection (Threat Command) (Intel).
Digital Risk Protection (Threat Command) Instance
Your subscription includes a single instance of the Digital Risk Protection (Threat Command) platform, provisioned for use by your organization. All authorized users from your security team shall be granted access to the data stored within this instance. Authorized users may also submit inquiries to the Ask an Analyst service, initiate remediation actions, authorize dark web purchase requests, and access additional services as defined within this Scope of Service.
Digital Risk Protection (Threat Command) conducts ongoing monitoring of a wide range of sources across the clear, deep, and dark web to identify potential threats associated with your organization’s digital footprint. The platform is designed to support timely and informed response to threats that may present significant risk to your business operations. Supported use cases include, but are not limited to: dark web monitoring, phishing protection, executive (VIP) protection, detection of data and credential exposure, ransomware disclosure monitoring, and fraud identification. Role-based access controls are supported to facilitate appropriate user permissions and data governance.